CYBERSECURITY / AUTOMATION / CURIOSITY

ABDELHAMID
MOULAY AISSA

SECURITY MONITORINGAUTOMATIONCOMPUTER ENGINEERING STUDENT

Understand the signals.
Connect the systems.
Build a more secure tomorrow.

Computer engineering student focused on security monitoring and automation. Explore my SOAR project and the training behind my technical foundations.

BASED IN MOROCCO ALWAYS LEARNING

sudomly@portfolio: ~BASH / PORTFOLIO

AM.SEC / INTERACTIVE PROFILE
Explore the person behind the projects.

$ welcome

Cybersecurity. Automation. Continuous learning.

Type help to list available commands.

Portfolio simulation · no system commands

01 / WHOAMI

A CURIOUS MIND.
A SECURITY MINDSET.

I'm Abdelhamid, a computer engineering student interested in understanding how systems work — and how to make them more secure.

My focus is on security monitoring and automation. Through SOAR, I explore how alerts, application logic, workflows and dashboards can support incident response.

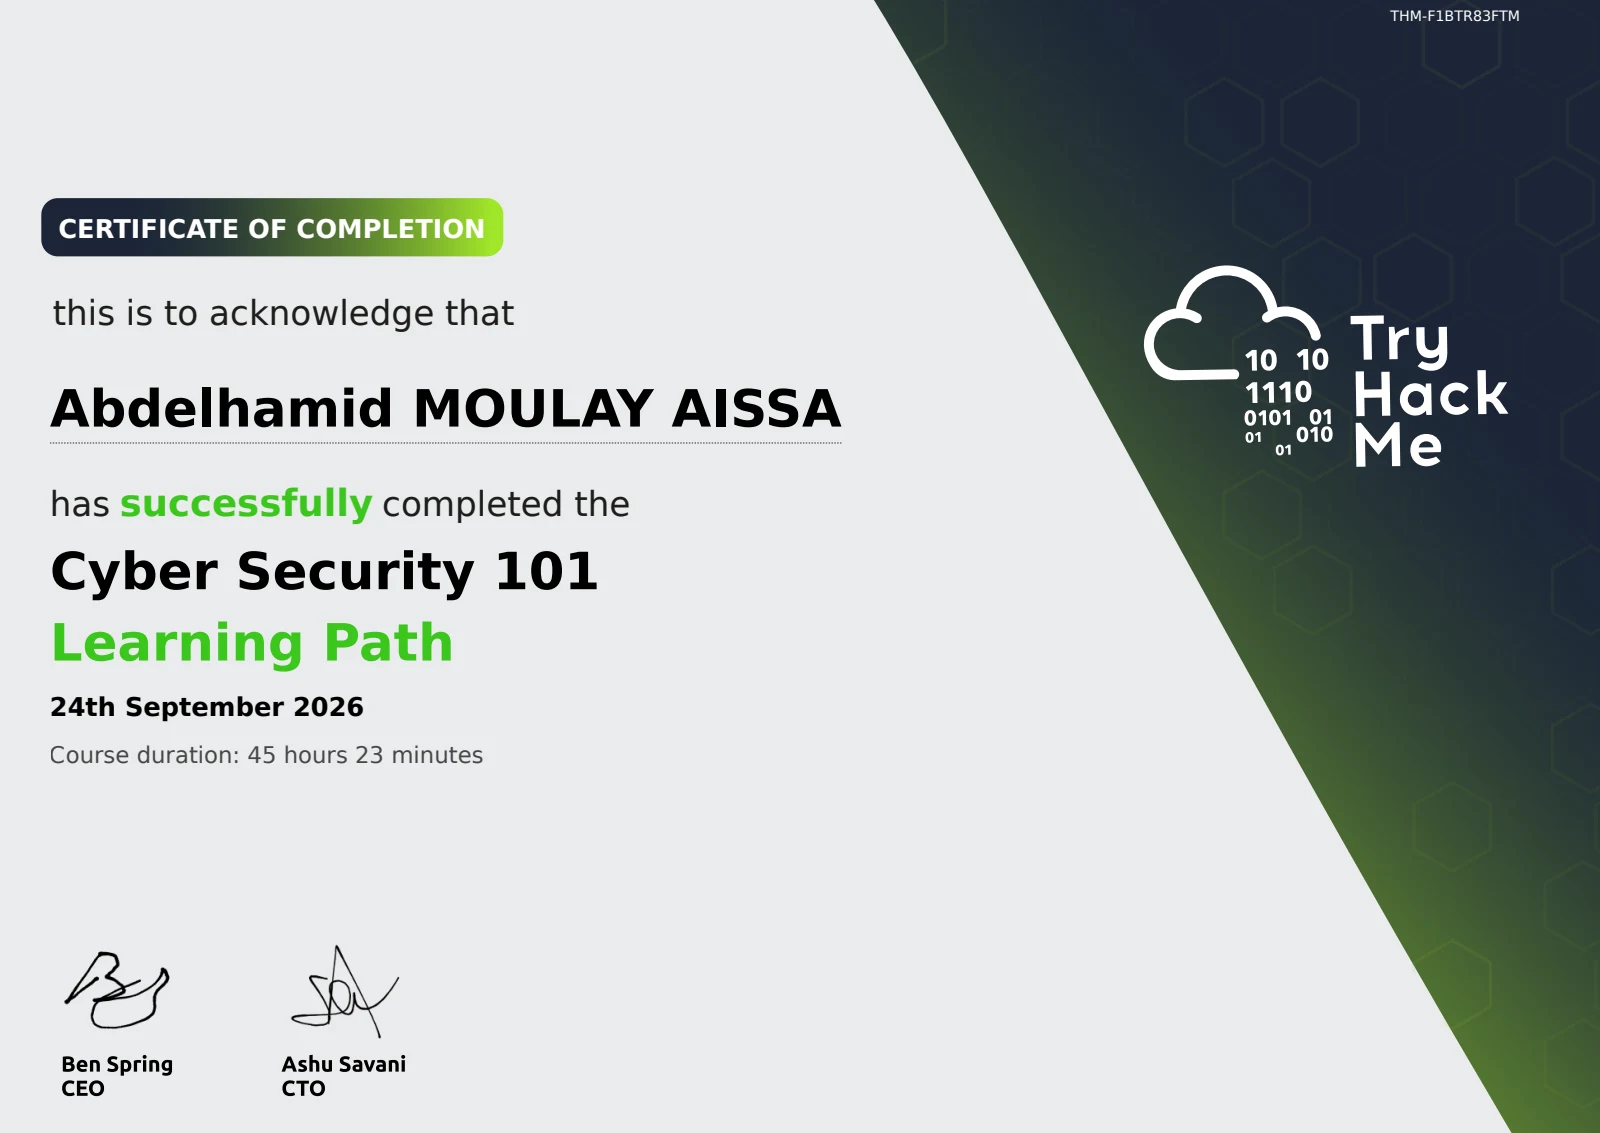
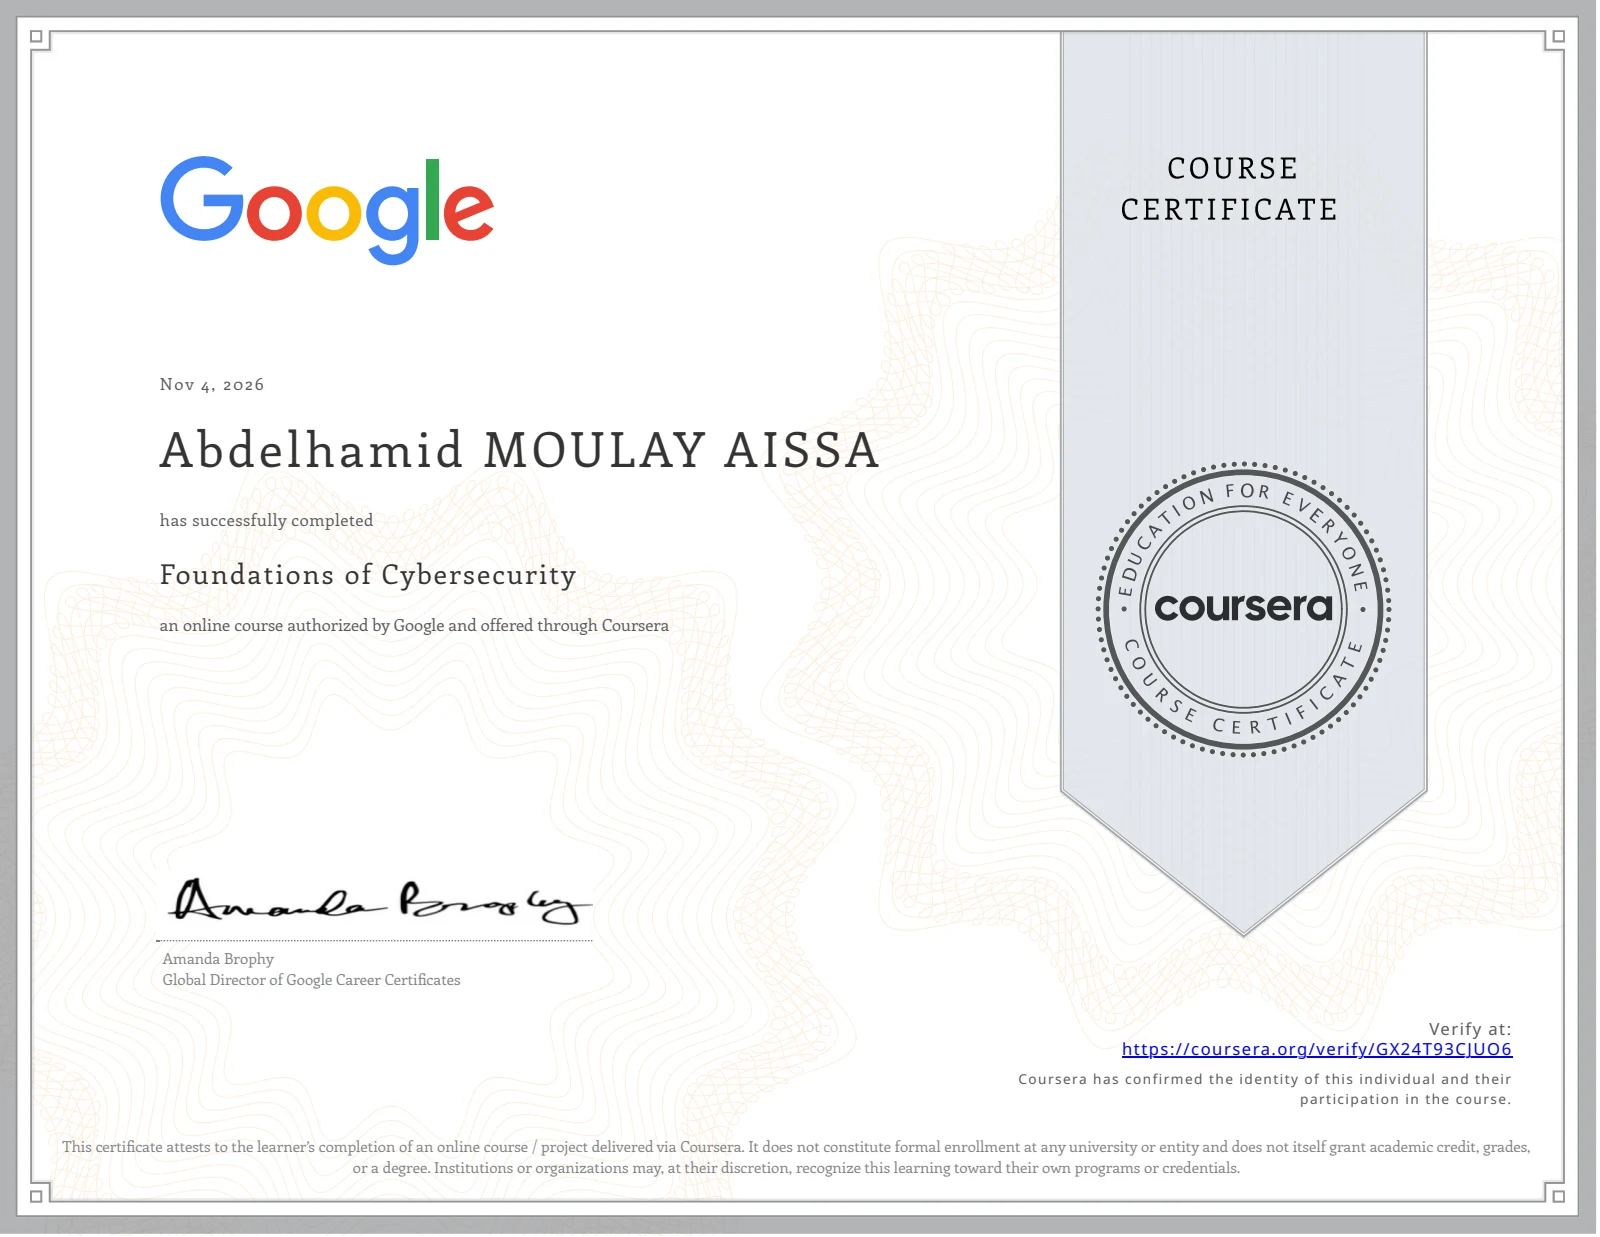
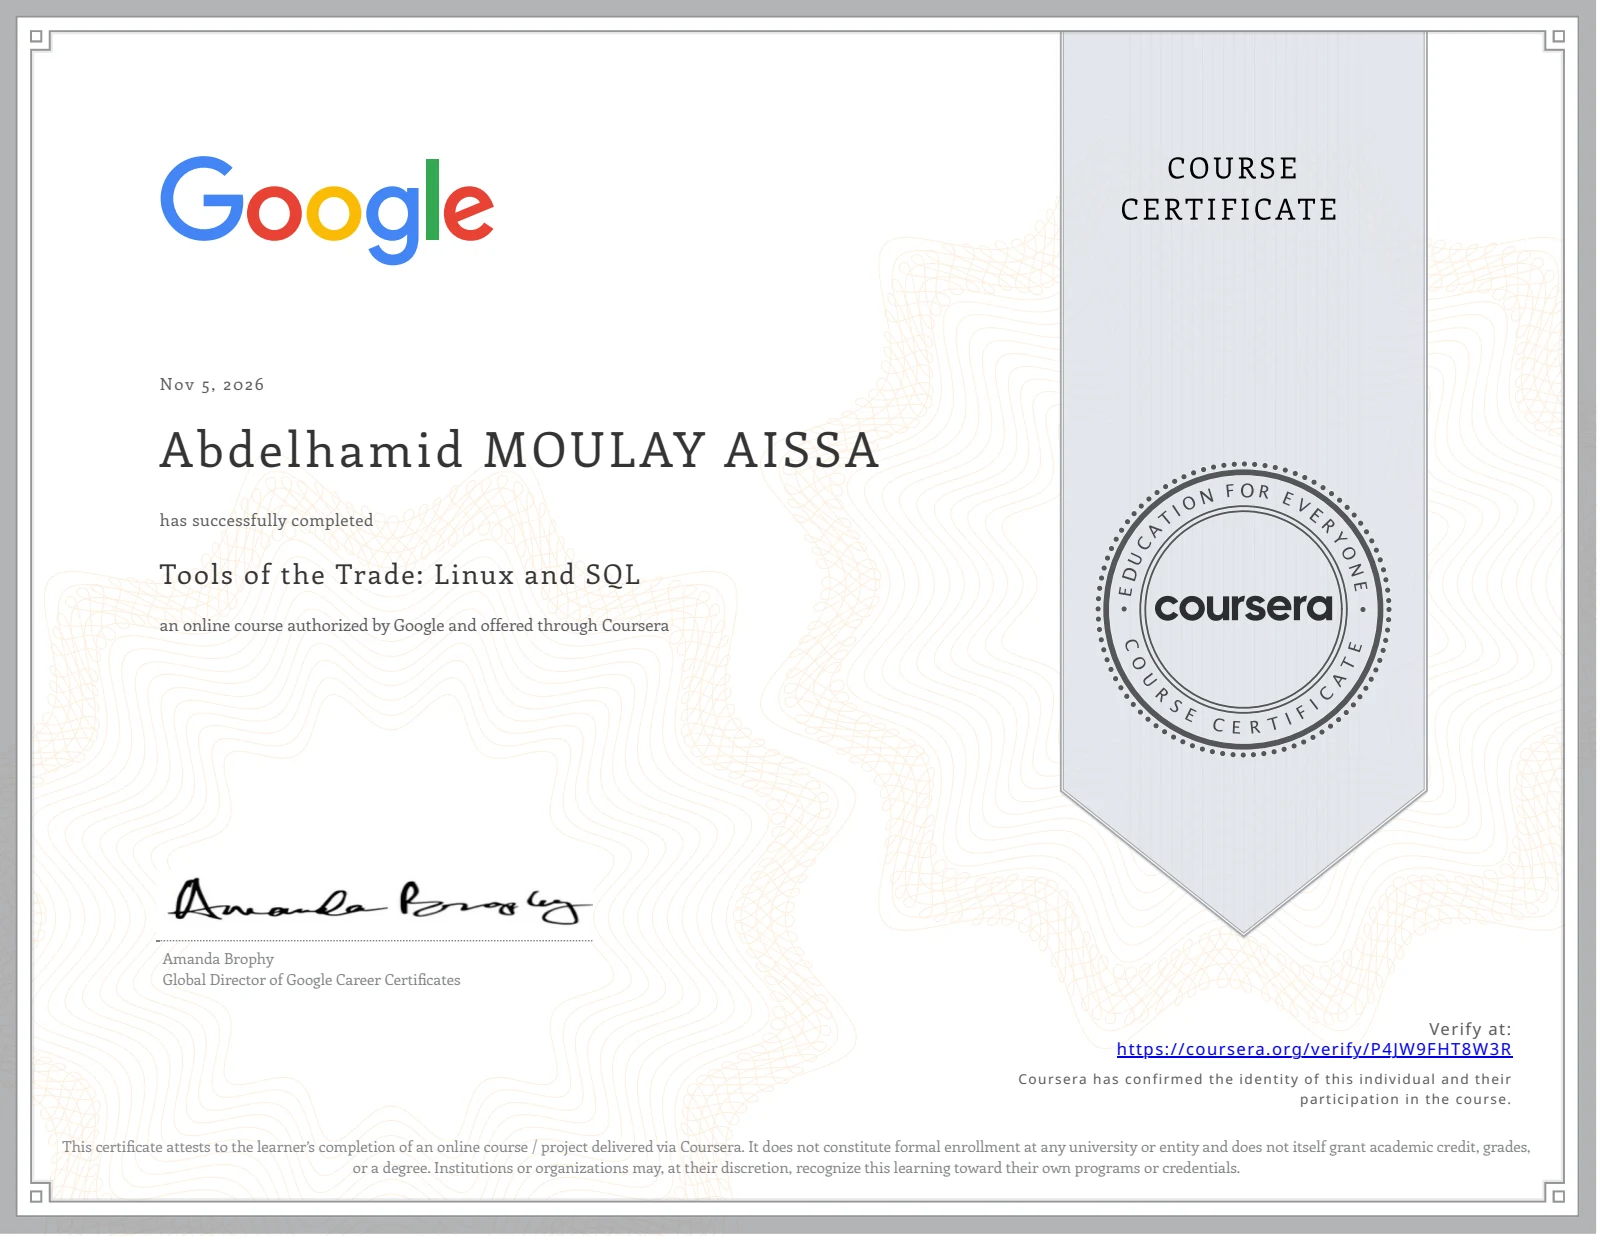
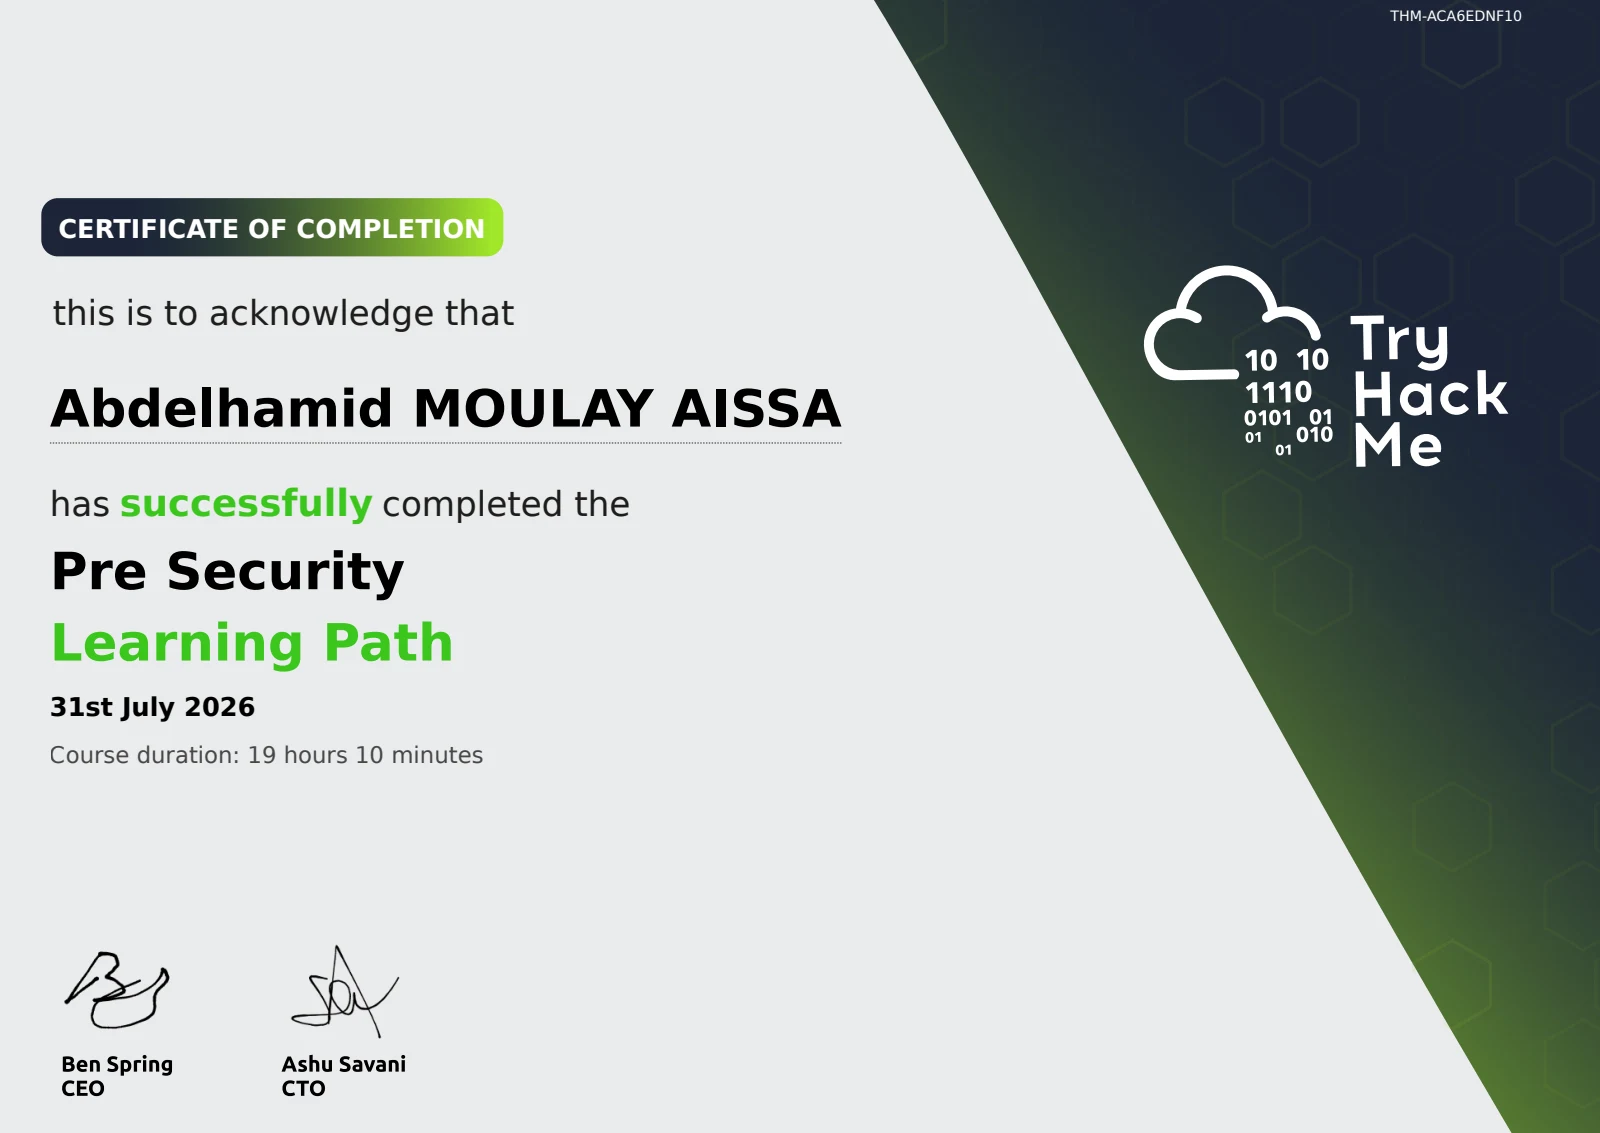
I build my foundations through practical projects and structured training, including TryHackMe learning paths and Google cybersecurity courses.

Explore my GitHub ↗

02 / SYSTEM CAPABILITIES

TECHNICAL ARSENAL.

Tools connected to my projects and completed training.

// SKILLS.LOG

CONTEXT OF USE — NOT PROFICIENCY SCORES

Wazuh / Security monitoring

Used in projects

Python / Flask

Used in projects

n8n / Workflow automation

Used in projects

PostgreSQL / Grafana

Used in projects

Linux / SQL foundations

Completed coursework

Cybersecurity foundations

Completed learning paths

// STACK.JSON

  • Wazuh
  • Python
  • Flask
  • n8n
  • PostgreSQL
  • Grafana
  • Linux
  • SQL

03 / PROJECT FILE

SOAR.
CONNECTING THE SIGNALS.

CASE 001 / SECURITY AUTOMATION

From alerts to understanding.

A security monitoring and automation project designed to analyze alerts, prioritize threats and support incident response.

The project brings together Wazuh monitoring, Python and Flask application logic, n8n workflows, PostgreSQL storage and Grafana visualization.

  • Wazuh
  • Python
  • Flask
  • n8n
  • PostgreSQL
  • Grafana

PROJECT FOCUS / SECURITY MONITORING & AUTOMATION

Read the project overview Browse my GitHub repositories ↗
SOAR / CONCEPT MAP
  1. 01 / MONITORSecurity signalsWazuh
  2. 02 / ORCHESTRATEAnalysis & workflowsPython · Flask · n8n
  3. 03 / UNDERSTANDData & visibilityPostgreSQL · Grafana

ILLUSTRATED ARCHITECTURE / NOT LIVE TELEMETRY
SOAR / PROJECT OVERVIEW

Turning security signals
into a clearer workflow.

SOAR stands for Security Orchestration, Automation and Response. This project explores how monitoring, application logic and connected workflows can support the investigation of security alerts.

Focus
Alert analysis & incident response
Approach
Connect monitoring, workflows & data
Perspective
Learning through practical projects

01 / THE CHALLENGE

An alert is a starting point.

A security signal needs context before it can guide a decision. The project focuses on connecting alert analysis with workflows, stored information and dashboards, so that the different parts of an investigation can be considered together.

02 / THE APPROACH

Give each tool a clear role.

Wazuh provides the monitoring layer. Python and Flask support application logic, while n8n connects workflow steps. PostgreSQL and Grafana bring persistent data and visualization into the picture.

How the stack fits together

A conceptual view of the project components.

Wazuh
MonitorSecurity monitoring and alerts form the starting point for analysis.
Python · Flask
ProcessApplication logic supports alert analysis and connects the project components.
n8n
OrchestrateWorkflows organize the steps involved in handling information.
PostgreSQL
StorePersistent data provides a foundation for reviewing information over time.
Grafana
VisualizeDashboards help present information for review and understanding.

WALKTHROUGH / ILLUSTRATIVE EXAMPLE

Following a suspicious sign-in signal.

This fictional scenario explains the workflow concept. It is not an actual incident, a test result or a demonstration of a deployed integration.

  1. Start with a signal

    A monitoring alert flags repeated unsuccessful sign-in attempts.

  2. Bring the context together

    Review the affected system, the event timing and the available alert information.

  3. Organize the review

    A workflow can help structure the next steps and keep relevant information together.

  4. Support a decision

    Stored information and a dashboard can support review. The signal alone does not establish that an account is compromised.

03 / LEARNING FOCUS

Understand the connections.

  • How monitoring signals become useful application inputs.
  • How workflows connect tools with distinct responsibilities.
  • How data storage and visualization support investigation.

04 / PROJECT SCOPE

Keep the evidence clear.

This overview describes the project focus and stack. It does not claim production deployment, measured response-time improvements or autonomous remediation.

For my public work and learning profile, visit GitHub.

Explore my public profile ↗

Explore the training behind the project.

View certifications & completed courses ↓

04 / VERIFIED LEARNING

THE CREDENTIAL VAULT.

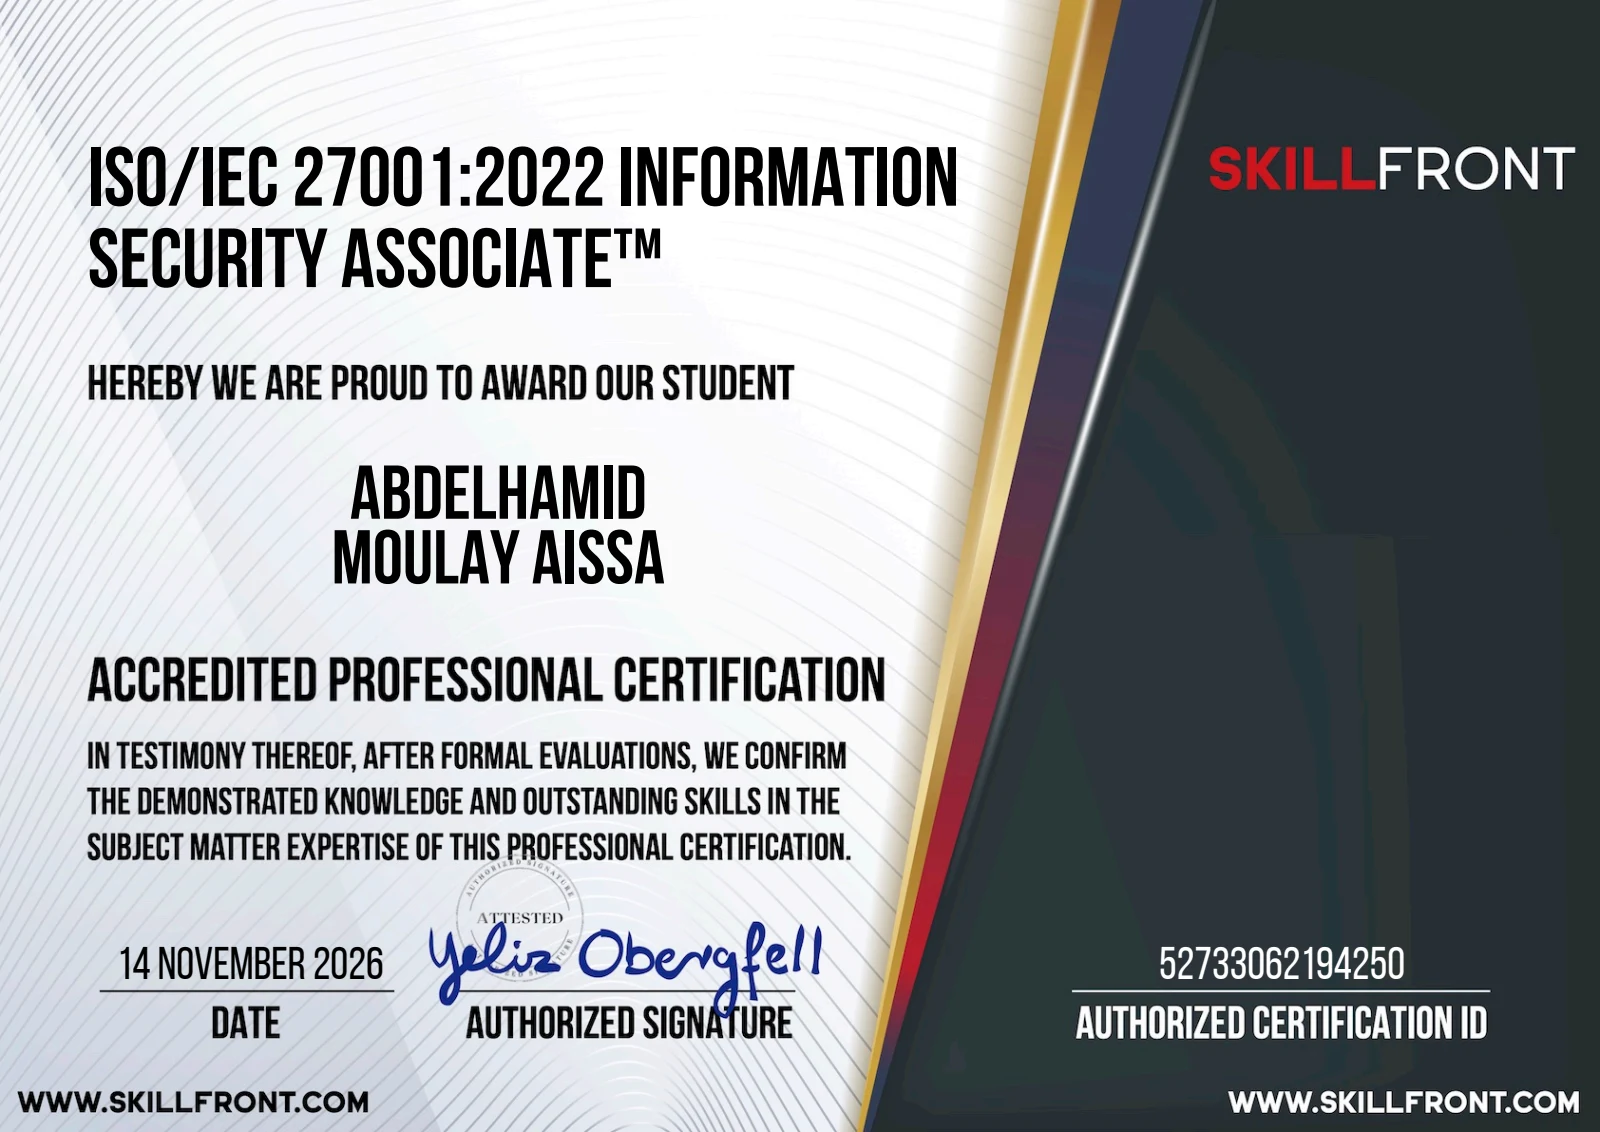
Completed certifications, learning paths and courses — with a continuing focus on cybersecurity.

IN PROGRESS

Google Cybersecurity Professional Certificate

Currently working toward the full professional certificate. The Google courses listed above are completed individual courses; the full credential has not yet been earned.

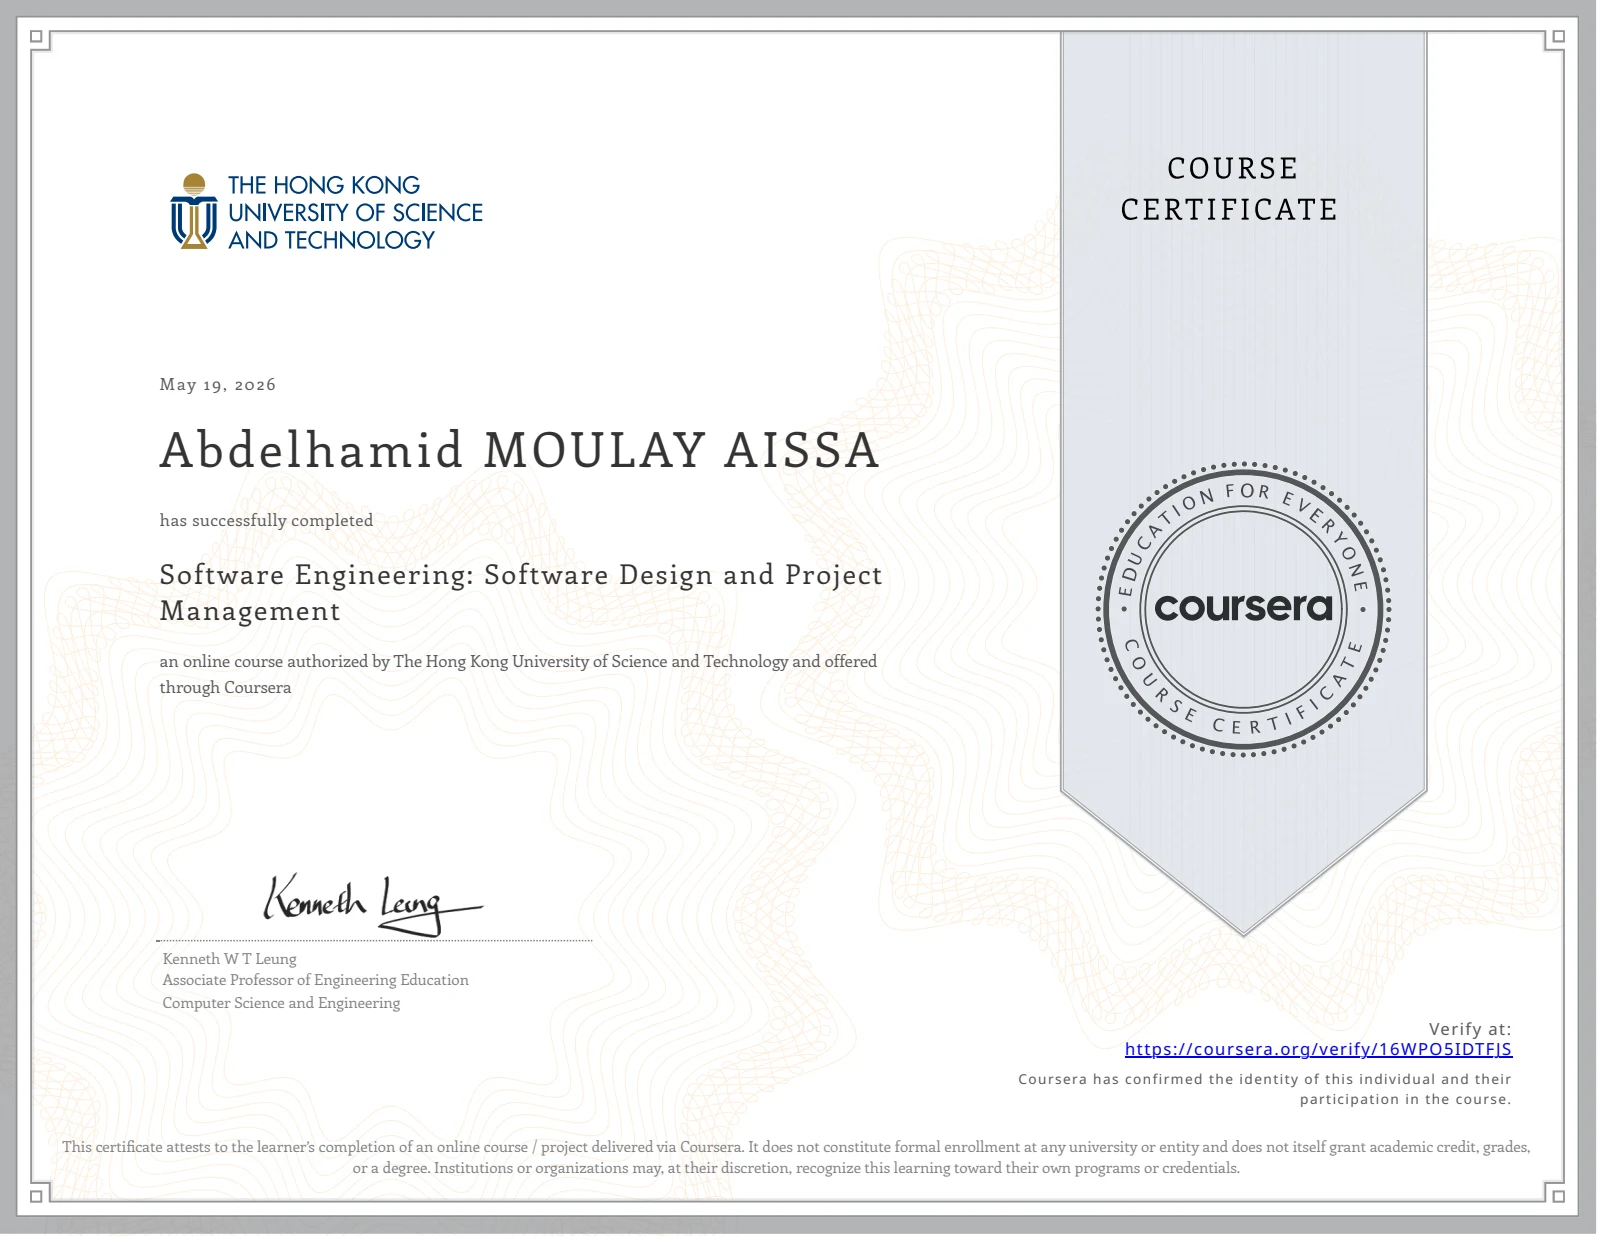
Additional training · Software engineering

05 / ESTABLISH CONNECTION

LET'S BUILD
SOMETHING SECURE.

Interested in security automation or my learning journey?
Explore my work and public profile on GitHub.

Connect on GitHub ↗

Certificate preview

Use the zoom button to inspect the certificate. Press Escape to close.